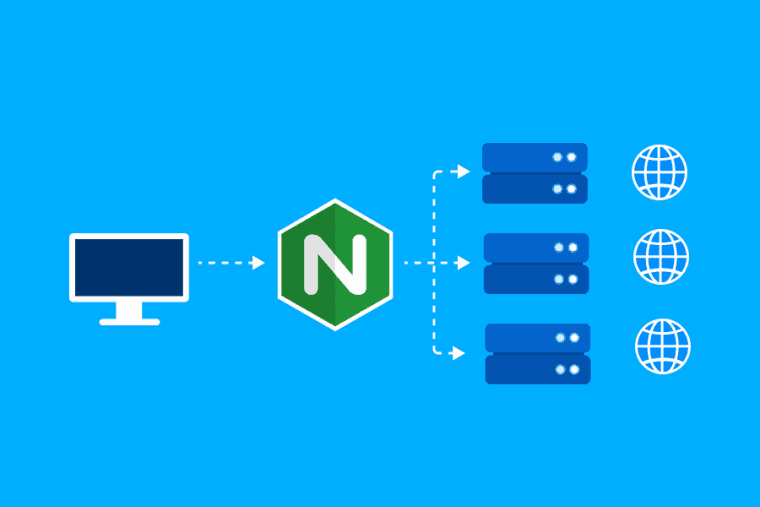
Visitors connect to a Nginx reverse proxy which connects to your application server . The requests are not coming directly to the backend, they are coming to Nginx and then Nginx is passing on the query to the relevant application.
This approach can improve security, scalability, traffic flow and performance. It is extensively used with Node.js, Laravel, Django, WordPress and other web applications.
What Is a Nginx Reverse Proxy?
A reverse proxy is a server that receives requests from clients and forwards the requests to one or more backend servers.
A typical setup would look like this:
              Visitors
                  |
                  v
              Nginx Server
                  |
        ---------------------
        |         |         |
      Node.js   Laravel   Django
      App       App       App
Visitors will be talking to Nginx and not directly to the application server. Nginx forwards the regular query to the correct backend.
This also allows the backend servers details to be hidden and provides a central place for handling SSL, caching, security rules and traffic management.
Why Use Nginx as a Reverse Proxy?
A Nginx Reverse Proxy provides several useful benefits.
Improved Security
Nginx adds an extra layer of security between your visitors and your application. Nginx can respond to requests from the outside world and back-end servers can be unreachable from the public internet.
The proxy level also allows you to define request limits, access rules and security headers.
Better Performance
Nginx can serve static files directly, without passing each query to the application. It can also cache to minimize repeated requests to the backend.
This is very useful if an application gets a lot of requests for the same content.
SSL Termination
Nginx can end HTTPS and forward the request over an internal connection to the backend.
The basic flow is as follows:
Visitor
   |
 HTTPS
   |
 Nginx
   |
 HTTP/HTTPS
   |
Application Server
This is what is called SSL termination. You can manage certificates from one central location.
Basic Nginx Reverse Proxy Configuration
Your first move is to install Nginx on your server and ensure your app is running on the backend port.
Say you’ve got a Node.js app running on port 3000.
A simple nginx config might be like:
server {
    listen 80;
    server_name example.com;

    location / {
        proxy_pass http://127.0.0.1:3000;

        proxy_set_header Host $host;
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }
}
Meanwhile, nginx will listen for requests to example.com and proxy them to the app on port 3000.
Test your configuration after modifying it, before reloading nginx:
sudo nginx -t
sudo systemctl reload nginx
Do that configuration before you do that. Always. There is syntax error in Nginx config, it will not reload correctly.
Proxy Headers
Proxy headers help your application understand information about the original visitor.
For example:
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Proto $scheme;
These headers can provide the original hostname, client IP address, and protocol information.
Your application should be configured to trust forwarded headers only when they come from trusted proxy servers.
Nginx Reverse Proxy for Node.js
Node.js applications commonly listen on an internal port such as 3000, while Nginx handles public HTTP and HTTPS traffic.
location / {
    proxy_pass http://127.0.0.1:3000;
}
Nginx can also provide SSL, caching, rate limiting, and access control without requiring every application to implement these features independently.
Nginx with Laravel and Django
Laravel applications are usually run using PHP-FPM and Django applications may be run with Gunicorn or another application server.
Nginx can sit in front of these and service public requests.
In a typical Laravel setup Nginx serves static files and forwards PHP requests to PHP-FPM.
To serve Django, route dynamic requests to Gunicorn through Nginx:
location / {
    proxy_pass http://127.0.0.1:8000;
}
The way you do this depends on your application’s structure and your deployment environment.
WebSocket Support
Applications using WebSockets require additional proxy headers.
For example:
location /socket/ {
    proxy_pass http://127.0.0.1:3000;

    proxy_http_version 1.1;
    proxy_set_header Upgrade $http_upgrade;
    proxy_set_header Connection "upgrade";
}
These settings make sure that Nginx maintains WebSocket connections open between the client and the backend application.
Caching and Load Distribution
Nginx can cache some responses to reduce load on back-end. Good for requested content often.
You can also configure Nginx for load balancing to multiple backend servers:
upstream backend {
    server 127.0.0.1:3000;
    server 127.0.0.1:3001;
}

server {
    location / {
        proxy_pass http://backend;
    }
}
In case one of the application servers (backends) fails, Nginx can redirect requests to another available backend using the configured loadbalancing method.
Common Troubleshooting Issues
Reverse proxy not working? First, check these out:
- Make sure your backend app is running.
- Backend for port scanning
- nginx configuration syntax error
- Look at the nginx error logs.
- Firewall rules testing
- Verify DNS records.
- Check the SSL Certificate Installation
- Proxy header validation
- Check the application logs
The 502 Bad Gateway error means that Nginx is not able to communicate properly to the upstream server.
Security Recommendations
Best practice is to keep ports for your back-end applications closed to the public internet. Access should be restricted to trusted services only.
Run public traffic in HTTPS Keep SSL certificates updated Lock down sensitive endpoints and use rate limiting if you can.
Do not put management interfaces on the Internet. Keep the application stack, the operating system and NGINX up-to-date to address known security issues.
Conclusion
An Nginx Reverse Proxy is a versatile buffer zone between your visitors and your app servers. It can terminate HTTPS, caching, load balancing, proxy headers and WebSocket connections while isolating backend services from the public traffic.
Nginx makes traffic a lot more manageable and gives you a much more solid base for a scalable, secure application, whether it’s Node.js, Laravel, Django or WordPress.