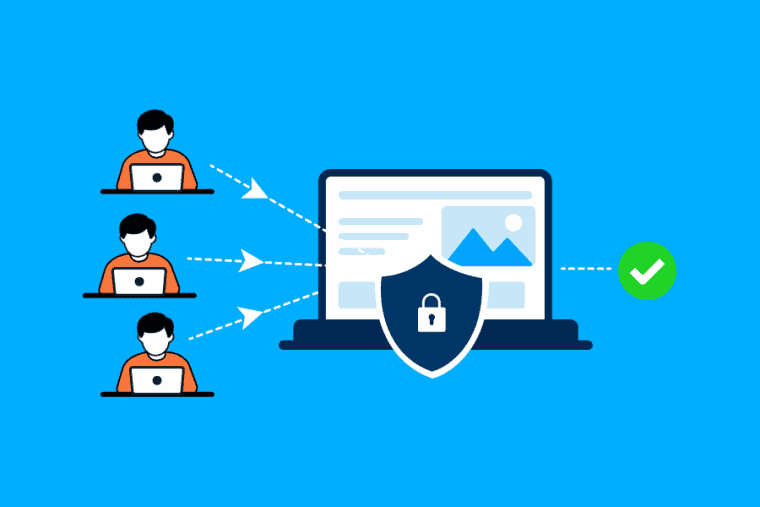
No website owner wants visitors to visit his website without interruption. But cyber attacks can quickly reverse that. DDoS Protection is crucial for keeping your website up and running, and preventing attackers from flooding your server with malicious traffic. Without the right protection, DDoS attacks can slow your site down, cause downtime and damage your business reputation.
The good news is that effective DDoS Protection may substantially mitigate these risks. In this guide you’ll learn what DDoS attacks are, how they work and how best to protect your website.
What Is a DDoS Attack?
A Distributed Denial of Service (DDoS) attack is when attackers use thousands or millions of compromised devices to create a huge amount of traffic to a website or server.
This server is currently busy. Please try again later. That means real visitors have to wait for the website to load or they can’t access it at all.
DDoS traffic is traffic that is purposely generated to take down your services. This isn’t a typical traffic spike from something going viral.
Common Types of DDoS Attacks
There are many ways you can attack your infrastructure, depending on the part.
Volume-Based Attacks
These attacks flood your network with a large amount of traffic until all of your available bandwidth is consumed.
Protocol Attacks
It attacks. Protocol attacks consume real network resources like firewalls and load balancers. They consume server resources and make the system unavailable.
Application Layer Attacks
These attacks are targeting specific parts of your website login pages search pages or checkout pages. They often look similar to real user requests and are hard to detect.
Why DDoS Protection Matters
A short power outage could be disastrous.
- Bad user experience
- Brand image damage
- Decreased consumer confidence
- Continued downtime will affect search engine rankings.
DDoS protection is much cheaper than the cost of recovery for companies that depend on online services.
Best Ways to Protect Your Website from DDoS Attacks
1. Use a Web Application Firewall (WAF)
A Web Application Firewall (WAF) checks incoming traffic before it reaches your website. It prevents the bad requests and lets good users connect.
Most modern WAFs also offer built-in DDoS protection and automatic threat detection.
2. Enable a Content Delivery Network (CDN)
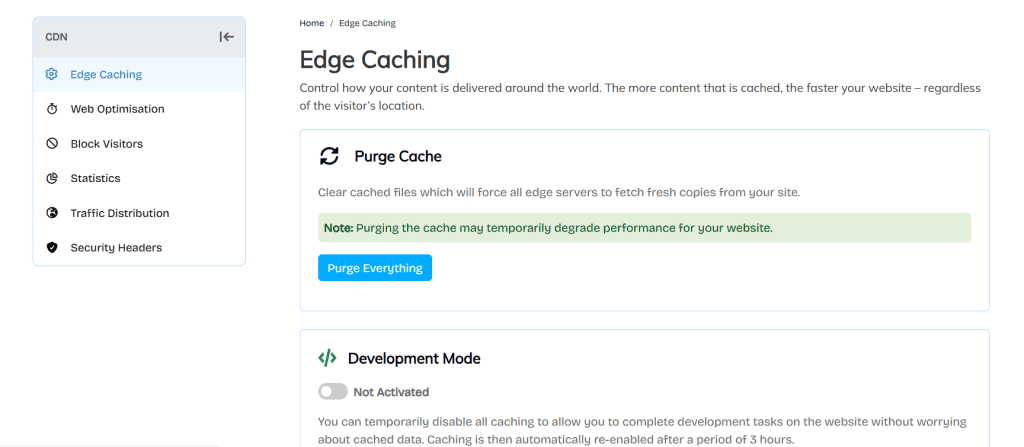
CDN is a network of many servers in various places to distribute your website.
Instead of sending all visitors to your main server , traffic is distributed throughout the CDN network . This helps to absorb large traffic spikes and DDoS impact, and to improve your site speed.
3. Implement Rate Limiting
Rate limiting is the limit of number of requests made by a user or an IP address in a certain period of time.
This can slow down or block traffic from an IP address sending 100s of requests per second.
This prevents attackers from flooding your site.
4. Monitor Your Server Continuously
The best defense is early detection.
Memory Usage CPU Usage Network traffic and bandwidth If you’re seeing sudden spikes this might be the start of a ddos attack.
Real-time monitoring allows your team to respond before an attack causes major disruption.
5. Filter Malicious Traffic
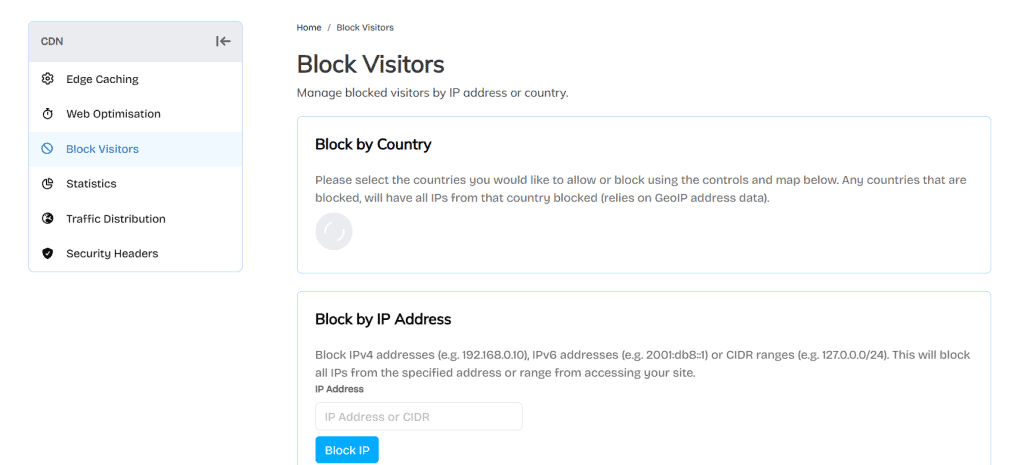
Traffic filtering makes it possible to isolate good visitors from bad requests.
Many companies that host websites or provide cloud security services will have intelligent filtering that blocks known bad IPs, bots and abnormal traffic patterns before they even hit your server.
6. Choose Hosting with DDoS Mitigation
Security – Provider dependent.
Seek out a provider that offers DDoS protection, firewall, network monitoring and automatic threat detection. These features add an extra layer of protection before attacks ever reach your site.
Real-World Example
Imagine an online store with a holiday sale. Then the site was attacked. Every second 1000 of fake requests were sent.
Without DDoS protection, customers can’t browse products or complete purchases. Sales close and visitors leave empty-handed.
If the website uses a CDN, Web Application Firewall and DDoS mitigation service, the malicious traffic is filtered before it reaches to the server. The real customers keep shopping and little disruption.
What to Do During a DDoS Attack
If your website is under attack, you need to act fast.
- Now get in touch with your host.
- If you can enable emergency DDoS mitigation.
- Block Bad IPs.
- Watch the server resources more closely.
- Please inform our customers if there will be any temporary delays in our services.
- Once the attack is over check server logs to see what happened.
An incident response plan can help reduce downtime and accelerate recovery.
DDoS Prevention Checklist
Use this checklist to make your website more robust.
- web application firewall (WAF)
- Use a trusted CDN
- Rate limiting parameters
- 24/7 Server Monitoring
- Update plugins and software.
- Block suspicious traffic automatically
- Choose a host that includes DDoS protection as a default.
- Regularly test your disaster recovery plan.
- Be sure you have a good backup
- Watch security logs carefully
Conclusion
As DDoS attacks grow larger and more frequent, website security has never been more important. You can’t eliminate all risk, but a good safety plan will go a long way toward decreasing the odds of downtime.
DDoS Protection includes several layers of protection such as Web Application Firewall, CDN, rate limiting, ongoing monitoring, traffic filtering and resilient hosting. These measures help keep your website up, protect your reputation, and ensure visitors can still get to your services when there are attempts to attack.