Linux Server Security Linux Server Security is crucial to safeguard websites, apps & databases from online attacks. Linux is secure by design, but no server is safe if you have weak passwords, outdated software or services that are misconfigured. Such problems can offer opportunities for hackers to gain unauthorized access or to launch cyber attacks.
Whether it is a personal VPS or a production server, following the right Linux server security practices can help mitigate such risks. In this tutorial we will go over the basic steps to secure your Linux server and give some useful command examples for Ubuntu, Debian and AlmaLinux.
Why Linux Server Security Matters
Compromised servers can lead to:
- Website unavailable
- Data Theft
- Malware infections
- Unauthorized access
- Search engine penalties
- Wasting money
A secure server protects your applications, your customer data, and your business reputation.
1. Keep Your Server Updated
Security updates fix newly discovered vulnerabilities. The best way to make your server more secure is to keep your operating system and any installed software up-to-date.
Ubuntu and Debian
sudo apt update
sudo apt upgrade -y
AlmaLinux
sudo dnf update -yIf available, turn on automatic security updates to help minimize the risk of missing important patches.
2. Secure SSH Access
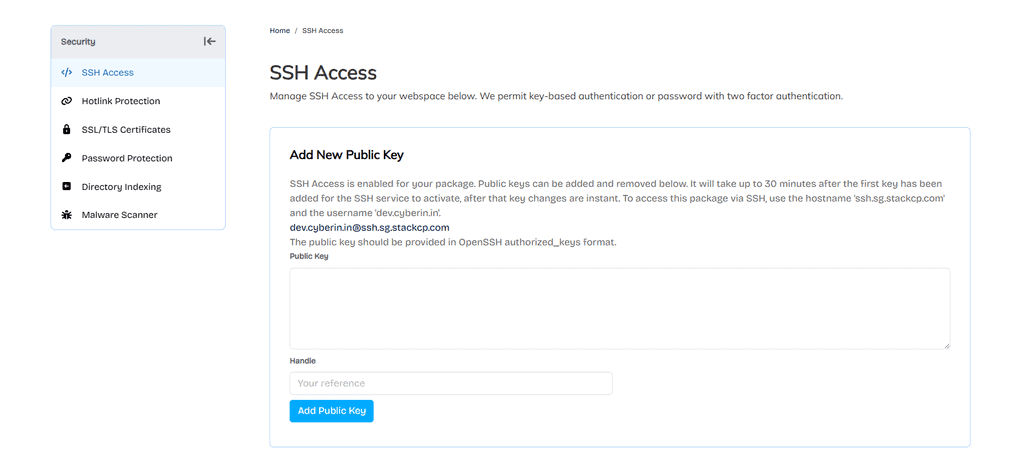
The main way of remotely controlling Linux servers is SSH, and it is a target of frequent attacks.
You can increase SSH security by:
- Changing the SSH Default Port
- Disable root logins
- Authentication based on SSH keys
- Set up SSH keys and turn off password authentication
Restart ssh for config changes
The SSH config file on Ubuntu, Debian and AlmaLinux is:
/etc/ssh/sshd_config3. Configure a Firewall
Firewalls can block off access to important services and stop unwanted network traffic.
Ubuntu and Debian (UFW)
sudo ufw allow OpenSSH
sudo ufw enable
AlmaLinux (Firewalld)
sudo systemctl enable firewalld
sudo systemctl start firewalld
Open only the ports your applications really need.
4. Use Strong User Permissions
Don’t use root for your day to day work.
Instead:
- Set up user accounts
- Only grant sudo rights when required.
- archive dormant accounts- Adhere to the principle of least privilege.
It helps reduce the risk of accounts being compromised.
5. Install Fail2Ban
Fail2Ban is software which bans an IP for a period of time after a number of failed login attempts, thus preventing brute-force attacks .
Install it on Ubuntu or Debian:
sudo apt install fail2banInstalling on Alma Linux
sudo dnf install fail2banOnce activated Fail2Ban will automatically monitor logins and ban suspicious activity.
6. Scan for Malware
Linux servers get malware, but not as much as Windows servers.
The most popular malware scanners:
- ClamAV
- Linux Malware Detect (LMD)
Regular scans can detect and block malicious files before they can do any damage.
7. Enable Automatic Backups
You need to get back to secure Linux server.
With good backups, if your server is compromised, you can get your website or app back up and running quickly.
Backup best practices:
- Backups (Daily)
- Off-site Storage
- Backup for routine testing
- Multiple restore points
8. Monitor Server Logs
System logs can be a gold mine of information about login attempts, application errors and suspicious activity.
Logs can be found in places like :
/var/log/auth.logor
/var/log/secureDepending on your Linux distribution it will be
Review logs routinely for anything out of the ordinary before it becomes a problem.
9. Enforce Strong Password Policies
Weak passwords are still one of the biggest threats to security today.
Passwords must contain:
- CAPITALS
- Small-cap stocks
- Figures 1.
- Other non alphanumeric characters
- minimum 12 characters
For server administration, use SSH keys instead of passwords wherever possible.
10. Use Intrusion Detection Tools
Intrusion detection systems safeguard your server from unauthorized modifications.
Some common tools are:
- AIDE – Advanced Intrusion Detection Environment
- OSSEC HIDS
- Wazuh (OSSEC)
These tools alert administrators to unauthorized modifications to critical files and configurations.
Troubleshooting Common Security Issues
SSH Access Lost
If that doesn’t work try to change the ssh settings:
- SSH configuration test
- Check firewall allows SSH.
- Restart sshd service Review all configuration changes before signing off.
Firewall Blocking Website
Ensure ports 80 (HTTP) and 443 (HTTPS) are open.
Failed Automatic Updates
Check your Internet connection, package repository settings, and try the updates again.
Linux Server Security Checklist
Before deploying your server, ensure that you have:
- All security updates are applied.
- root login disabled, use sudo i
- Set up SSH Key Authentication
- Firewall is enabled.
- Fail2ban is installed
- Set strong password policies
- Backups are automatically configured
- configured malware scanning tools
- Logging in
- Remove no longer required services
- Limited user rights
- Scheduled maintenance (periodic)
This checklist will help you avoid common security pitfalls and strengthen the security of your server.
Conclusion
Maintenance is good security. Regular updates, secure ssh settings, firewalls, good user permissions, Fail2Ban, backups and log monitoring can help keep your server safe from common threats.
No matter if you are running a small VPS or enterprise infrastructure, you are able to implement these best practices to reduce downtime and secure your websites and applications and keep your websites and applications running securely.
Frequently Asked Questions
1. Why is Linux server security important?
It also protects your server against unauthorized access, malware, data theft and service interruptions.
2. Is a firewall necessary on Linux?
Yep. . Firewalls are used to restrict access to approved services and block unwanted traffic.
3. What is Fail2Ban?
Fail2Ban is a security application that attempts to block IPs after a number of failed login attempts, so as to prevent brute force attacks.
4. Should I disable root SSH login?
Yes, disabling root login to a server is more secure and it prevents unauthorized access.
5. How often should I update my Linux server?
Apply security updates as soon as they become available. Stay tuned to your server for updates.